Cross-border digital fraud is a nightmare for local law enforcement. When a scammer sitting in a foreign jurisdiction drains a victim's bank account or orchestrates an online extortion racket across multiple servers, local police usually hit an immediate wall. Jurisdictional boundaries stop investigations cold.
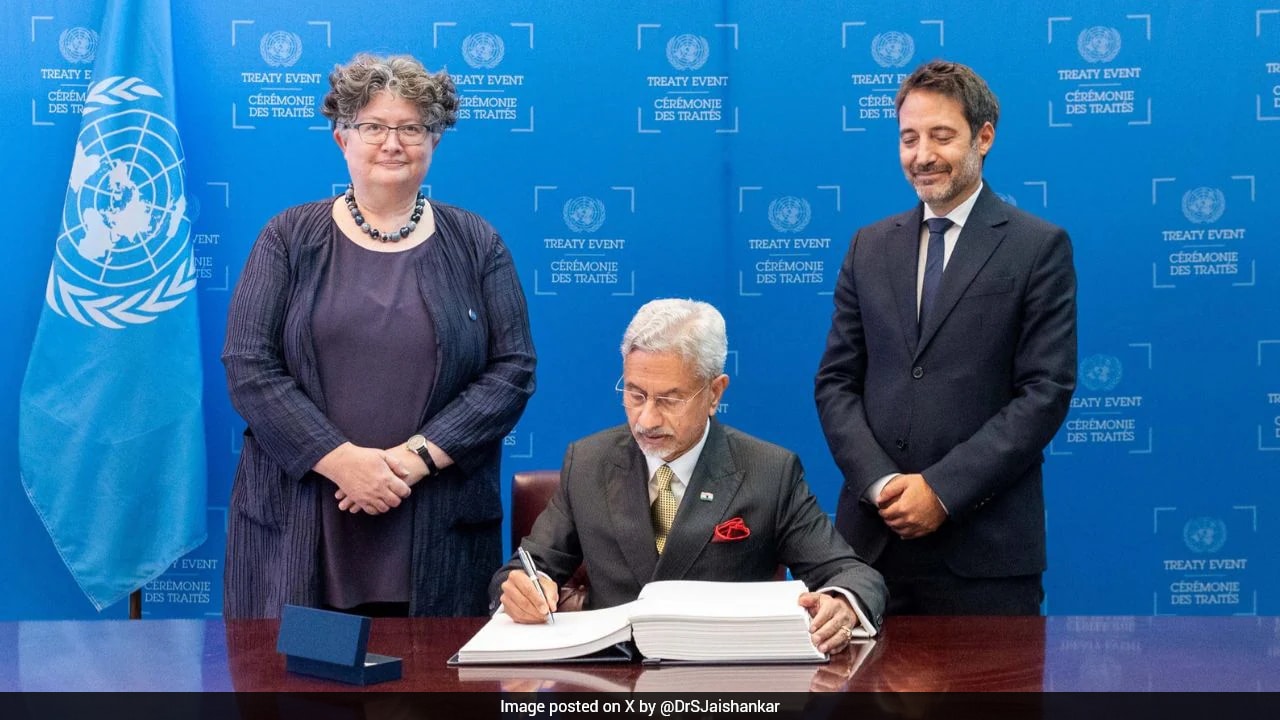
External Affairs Minister S. Jaishankar's decision to sign the United Nations Convention against Cybercrime on the sidelines of the 81st UN General Assembly attempts to smash through those walls. It's a massive move for India's digital security strategy, bypassing decades of bilateral bureaucratic gridlock to establish a unified global playbook against cyber-enabled crime.
Breaking Down the UN Cybercrime Treaty
The formal name of the treaty is a mouthful: the United Nations Convention against Cybercrime, Strengthening International Cooperation for Combating Certain Crimes Committed by Means of Information and Communications Technology Systems and for the Sharing of Evidence in Electronic Form. Adopted by the UN General Assembly, the framework focuses heavily on practical operational hurdles that investigators face daily.
Criminals don't care about borders. Your data might pass through three foreign servers before a fraudulent transaction hits a mule account overseas. This convention creates mechanisms to streamline how electronic evidence is shared across countries.
Instead of waiting months through traditional Mutual Legal Assistance Treaties (MLATs), the treaty establishes a round-the-clock network. Law enforcement agencies can coordinate swiftly when every minute counts in tracking stolen capital.
Why This Matters for India Right Now
India faces a staggering volume of digital fraud, ranging from sophisticated investment scams to remote extortion rings operated by syndicates rooted outside domestic borders. Domestic cyber cells frequently trace digital money trails right up to an international boundary, only to watch investigations stall because foreign local police lack the incentive or obligation to cooperate.
By signing this pact, India aligns itself with a growing multilateral consensus. Notably, India chose to sign this comprehensive UN instrument rather than acceding to the older, Western-centric Budapest Convention. This gives Indian agencies a recognized framework to demand cooperation, trace financial proceeds, and reclaim stolen money moving through shell accounts globally.
As cybercrime expert and former IPS officer Triveni Singh has pointed out, international collaboration remains the single biggest missing link in stopping digital financial crime. Without standardized channels for electronic evidence, fraudsters operate with virtual impunity.
The Balancing Act Between Security and Privacy
Any treaty dealing with cross-border digital surveillance and electronic evidence sharing invites fierce debate. Human rights organisations and digital privacy advocates have raised valid concerns since negotiations began.
When governments build global networks to share digital evidence quickly, the risk of overreach grows. The line between tracking a transnational financial scammer and enabling state surveillance on political speech or dissent can easily blur if safeguards aren't strictly enforced.
For India, implementing this treaty domestically will require robust judicial oversight. Collecting electronic evidence across borders must comply with domestic privacy standards while maintaining the speed required to catch fast-moving financial predators. Signing the treaty is merely the starting gun; the real test lies in how national legislation handles data protection during cross-border investigations.
Practical Next Steps for Security Teams and Organizations
If you run a business or manage enterprise infrastructure, international treaties might feel distant from your daily security operations. They aren't. Global legal harmonization changes how incident response works during large-scale attacks.
- Audit your cross-border data flows: Understand where your user and operational data is stored, and how third-party vendors handle multi-jurisdictional compliance.
- Strengthen electronic evidence preservation: Ensure your incident response logs meet strict chain-of-custody standards. When law enforcement requests digital artifacts for an international investigation, clean and verifiable logs prevent technical delays.
- Monitor treaty ratification milestones: Keep an eye on how domestic enforcement agencies translate these international cooperation frameworks into actionable standard operating procedures over the coming months.