The operational security architecture surrounding forward-deployed strategic airbases relies on a fragile continuum between local law enforcement and national intelligence apparatuses. When state-backed asymmetric operations target dual-use military installations, the resulting friction exposes critical seams in threat attribution, inter-agency communication, and the threshold required for public disclosure. The investigation surrounding the foiled security threat at Royal Air Force Fairford in Gloucestershire illustrates the structural vulnerabilities inherent in modern counter-terrorism intelligence sharing and state-proxy conflict management.
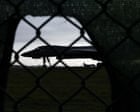
Deconstructing the Fairford incident requires examining the operational vectors utilized by hostile state actors against Western military infrastructure. Modern power projection depends heavily on strategic hubs like RAF Fairford, which serves as a critical European staging ground for heavy bomber operations. Consequently, these installations are primary targets for intelligence disruption, reconnaissance, and sabotage campaigns orchestrated by adversarial states via localized proxies. Learn more on a connected issue: this related article.
The incident unfolded through a classic low-signature operational footprint: local operatives utilizing commercial transport vehicles to position volatile materials near perimeter boundaries. The mechanism of detection—a routine civilian observation rather than an automated signals intelligence interception—underscores a fundamental vulnerability in military base perimeter security. Intelligence services face a permanent monitoring cost function: maintaining total situational awareness across sprawling rural perimeters is economically and physically prohibitive, forcing reliance on layered defense models that frequently fail at the lowest layers of human detection.
State attribution in asymmetric sabotage operations follows a distinct political and evidentiary trajectory. The public assertion by United States Secretary of State Marco Rubio that a foreign actor was clearly behind the plot, juxtaposed against the initial police caution and subsequent bail decisions by British judicial authorities, highlights a chronic divergence in risk tolerance and evidentiary standards between intelligence-sharing allies. Additional reporting by The Guardian highlights similar views on this issue.
This divergence is governed by two competing operational imperatives:
- The Intelligence Protection Imperative: Domestic law enforcement agencies operate under strict evidentiary requirements designed to secure convictions in open courts, necessitating the preservation of sensitive sources, methods, and forensic certainty before formal charges can be sustained.
- The Strategic Deterrence Imperative: National security leadership often prioritizes rapid public attribution to signal awareness to the adversary, deter subsequent attacks, and rally political cohesion, even when public-facing evidentiary dossiers remain incomplete.
The decision by British authorities to release suspects on bail triggered immediate friction between Washington and London. From a strict investigative standpoint, bail does not imply exoneration; rather, it reflects a calculated operational choice by counter-terrorism detectives who assess that the immediate threat vector has been neutralized, allowing them to monitor suspects rather than prematurely compromise a wider network. However, from a geopolitical signaling perspective, releasing individuals linked to a state-sponsored kinetic threat creates strategic ambiguity and undermines the deterrent posture required in an active theater of proxy confrontation.
Furthermore, the operational calculus of state-backed proxies relies on plausible deniability. By employing localized non-state actors or criminal surrogates to procure logistical supplies—such as fuel containers and metallic shrapnel components—foreign intelligence services insulate themselves from direct attribution while testing the speed and efficacy of host-nation counter-terrorism responses. When these plots are disrupted, the absence of direct state insignia forces a reliance on behavioral patterns, communications intercepts, and financial tracing to establish the chain of command back to the sponsoring regime.
To elevate the security posture around forward operating bases against persistent proxy infiltration, military and domestic security planners must restructure their defensive frameworks around three core operational shifts. First, intelligence fusion centers must integrate civilian infrastructure reporting directly into military threat matrixes, closing the gap between local eyewitness anomalies and national security databases. Second, bilateral intelligence-sharing protocols must standardize attribution thresholds to prevent public messaging discrepancies between allied nations during active investigations. Third, perimeter defense architectures must transition from passive physical barriers to active, multi-spectral sensor grids capable of autonomously distinguishing between innocuous civilian traffic and coordinated reconnaissance vectors before a breach can materialize.